


Disclosure: On this site you won’t find specific advice on “how to call function xyz()”. Interpreting C++ ARM and #pragma dwim is also out of scope.
We’re treating our readers as intelligent beings who can use Google and/or StackOverflow, where all such specific questions were answered more than once.
What you will find is opinions, more opinions, and even more opinions on all the aspects of software development - and with a large chunk of them based on real-world experience too.
Your mileage may vary. Batteries not included.
Journaled Flash Storage – Emulating EEPROM over Flash, ACID Transactions, and More. Part I – Flash vs EEPROM
September 28, 2015 by • “No Bugs” Bunny
Quote:
You cannot erase single byte of Flash, but need to erase the whole page
Another Quote:
First of all, we want to be sure that whatever-is-already-written to our persistent storage, stays there; this property is known as Durability.
Filed under: On.ProgrammingEmbeddedOn.HardwareMCU
Read moreModified Harvard Architecture: Clarifying Confusion
September 21, 2015 by • “No Bugs” Bunny
Abstract:
Definition of "Modified Harvard" architecture is confusing and overbroad. Proposed alternatives are "Almost-Harvard" and "Almost-von-Neumann
Quote:
"One thing nobody realised for a while is that the system with the least possible amount of chargebacks is the system which rejects all transactions outright
Filed under: On.ProgrammingEmbeddedOn.HardwareMCU
Read moreAddressing the Delayed Message Attack in Wireless IoT Environments
September 14, 2015 by • “Sergeant Major” Hare
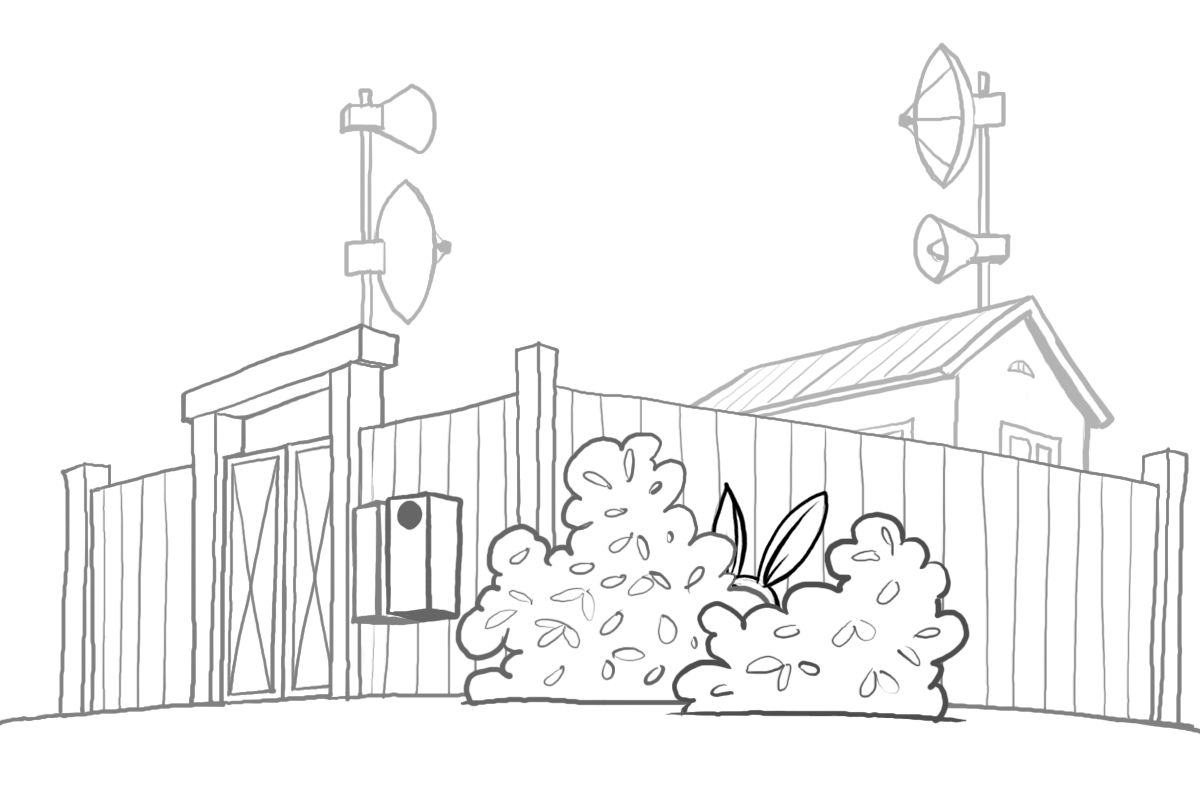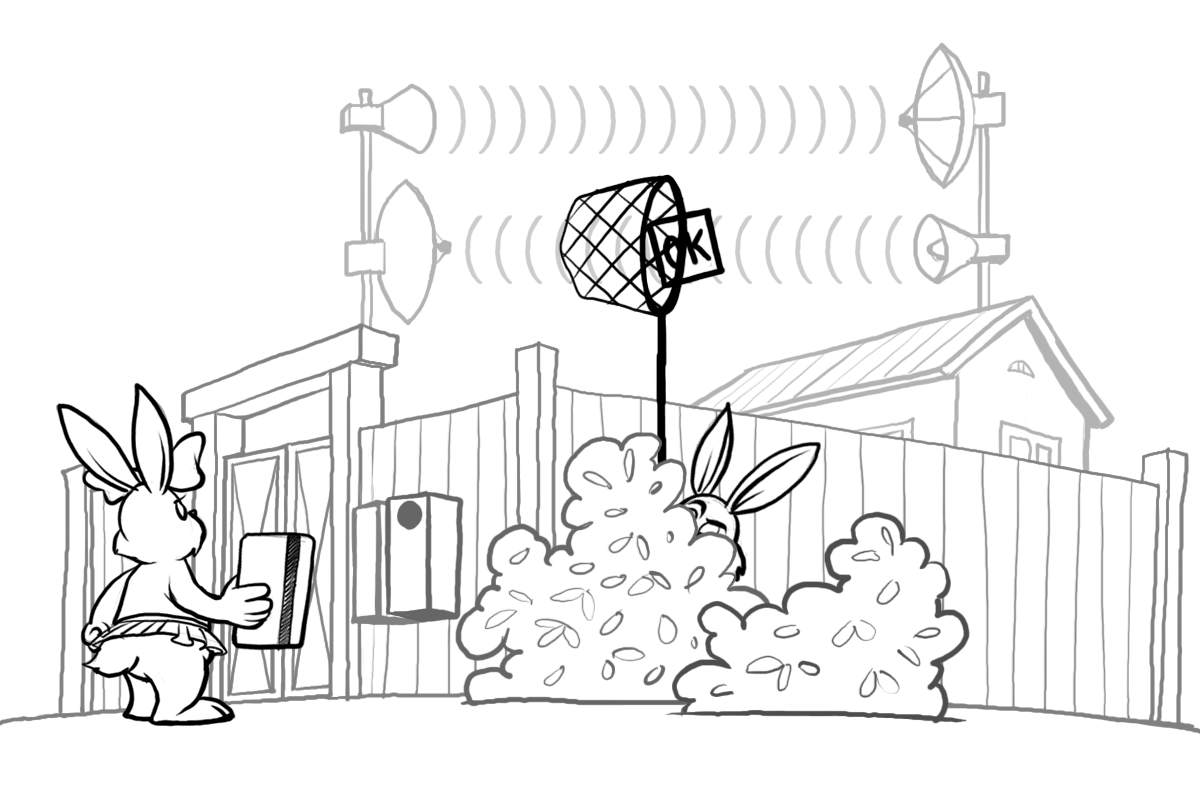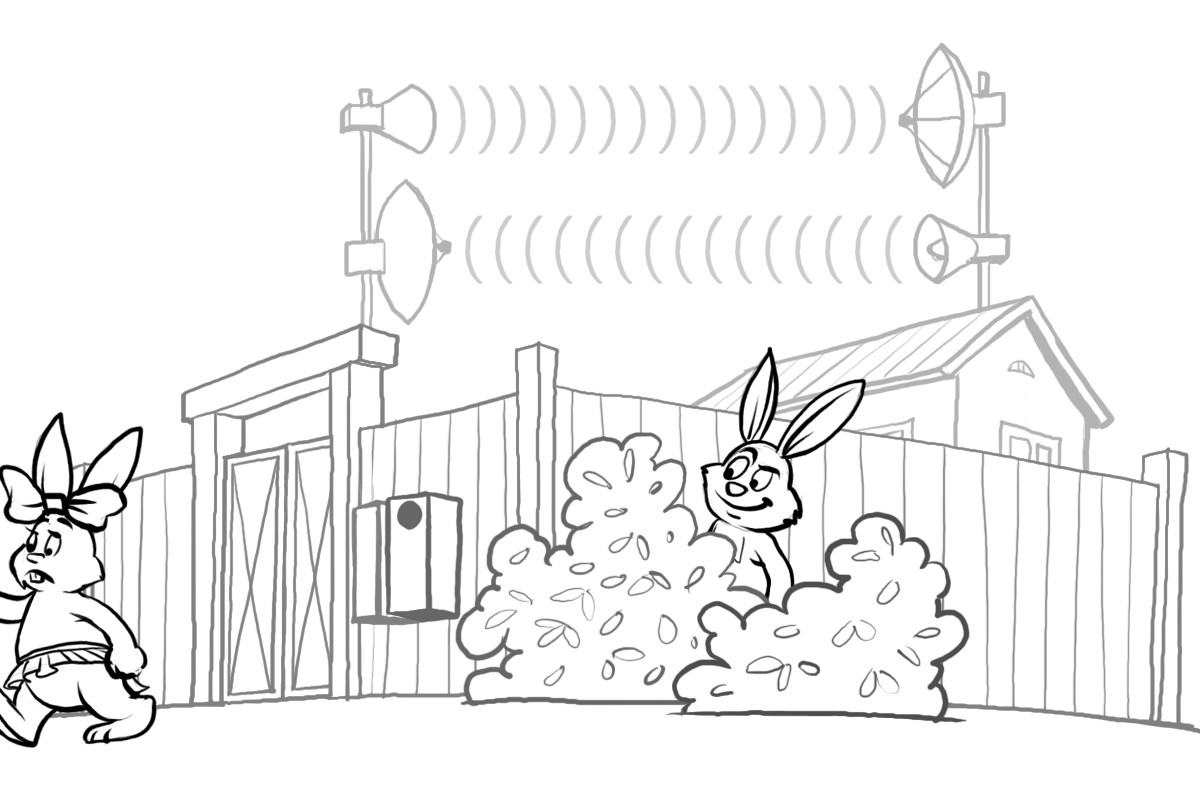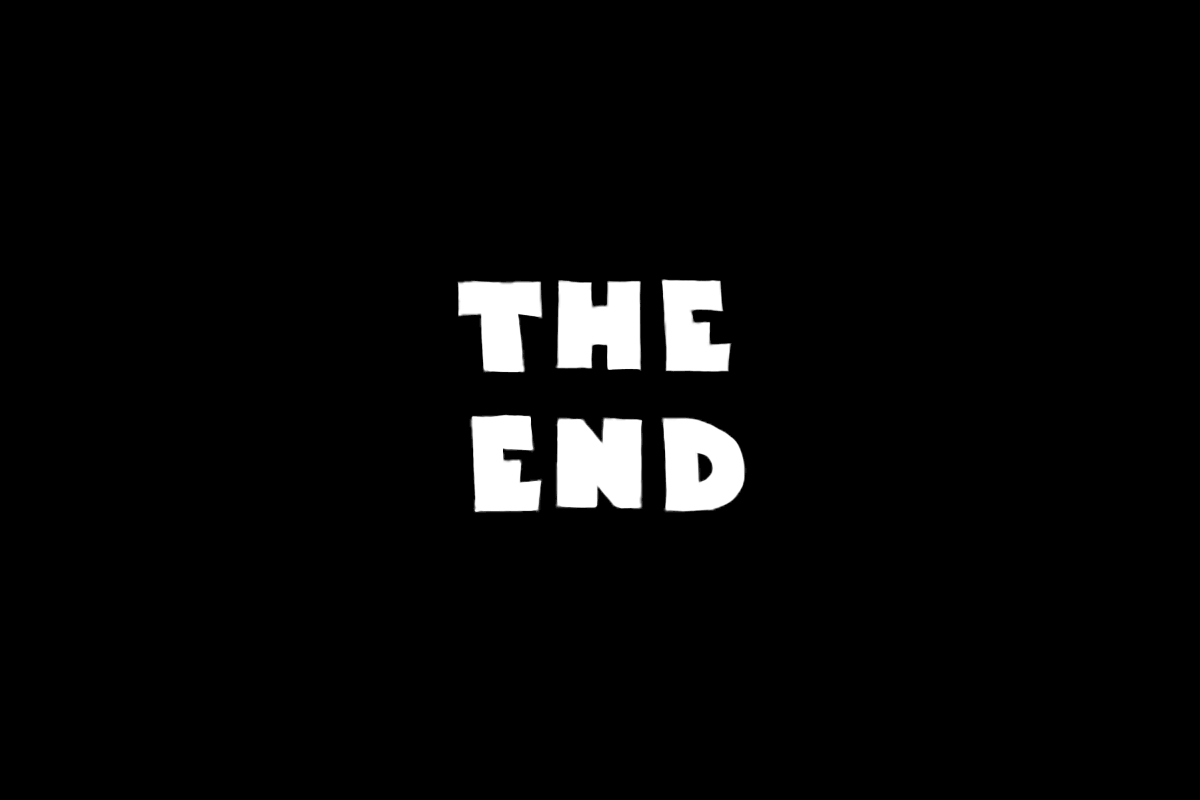
Abstract:
Delayed-Message Attacks can Represent a Real Threat if Left Unchecked
Quote:
Prevention/mitigation of the Attack is easy, but it needs to be taken into account at the application level.
Filed under: On.SecurityResearch
Read moreMulti-threading at Business-logic Level is Considered Harmful
September 7, 2015 by • “No Bugs” Bunny
Quote:
However, the window for triviality is very narrow: for example, even going into two interrelated mutexes instead of one, can easily make multi-threading non-trivial
Another Quote:
Technically you are able to jump to any point of your program, but the variables you see may (and if you have a multi-threaded bug – will) differ every time you jump there.
Filed under: On.System ArchitectureDesign decisionsOn.ProgrammingDebugging
Read more
Six Impossible Things Before Breakfast Ltd. © 2026. All rights reserved.

